In this blog, we will address the most important topics that your IT-colleagues look at when approving a new project.
Bart Valks

You’re about to get your project started! After months of getting colleagues aboard, finding internal budget and looking for the right supplier, you feel like you are nearly there. You have a proposal to be approved, and then… all of a sudden your director enters your office, and explains that the IT department needs to approve the proposal before he can sign off, and his last approval cycle took two months! Darn… what now?
Does this sound at all familiar? If so, this blog is for you! We are going to outline what IT might be looking for, and how you can get your approval through as soon as possible. It’s not as hard as you may think…
Data protection
You might have heard these abbreviations come by in conversations: GDPR (General Data Protection Regulation) or DPIA (Data Protection Impact Assessment). The GDPR is the European Union’s regulation on information privacy. A DPIA is an instrument to assess the impact of data processing when personal data is involved. When these terms are in play, the underlying goals are (1) to prevent the collection of personal data and/or (2) to limit the risks when processing personal data.
When it comes to the processing of personal data, you can limit or even avoid its collection entirely. With our preferred sensor technology, we can categorically state that no information is collected which can make persons identifiable. Furthermore, in booking and scheduling systems we can avoid the processing of personal data, such as the name of the booking holder or name(s) assigned to activities.
Safe connectivity
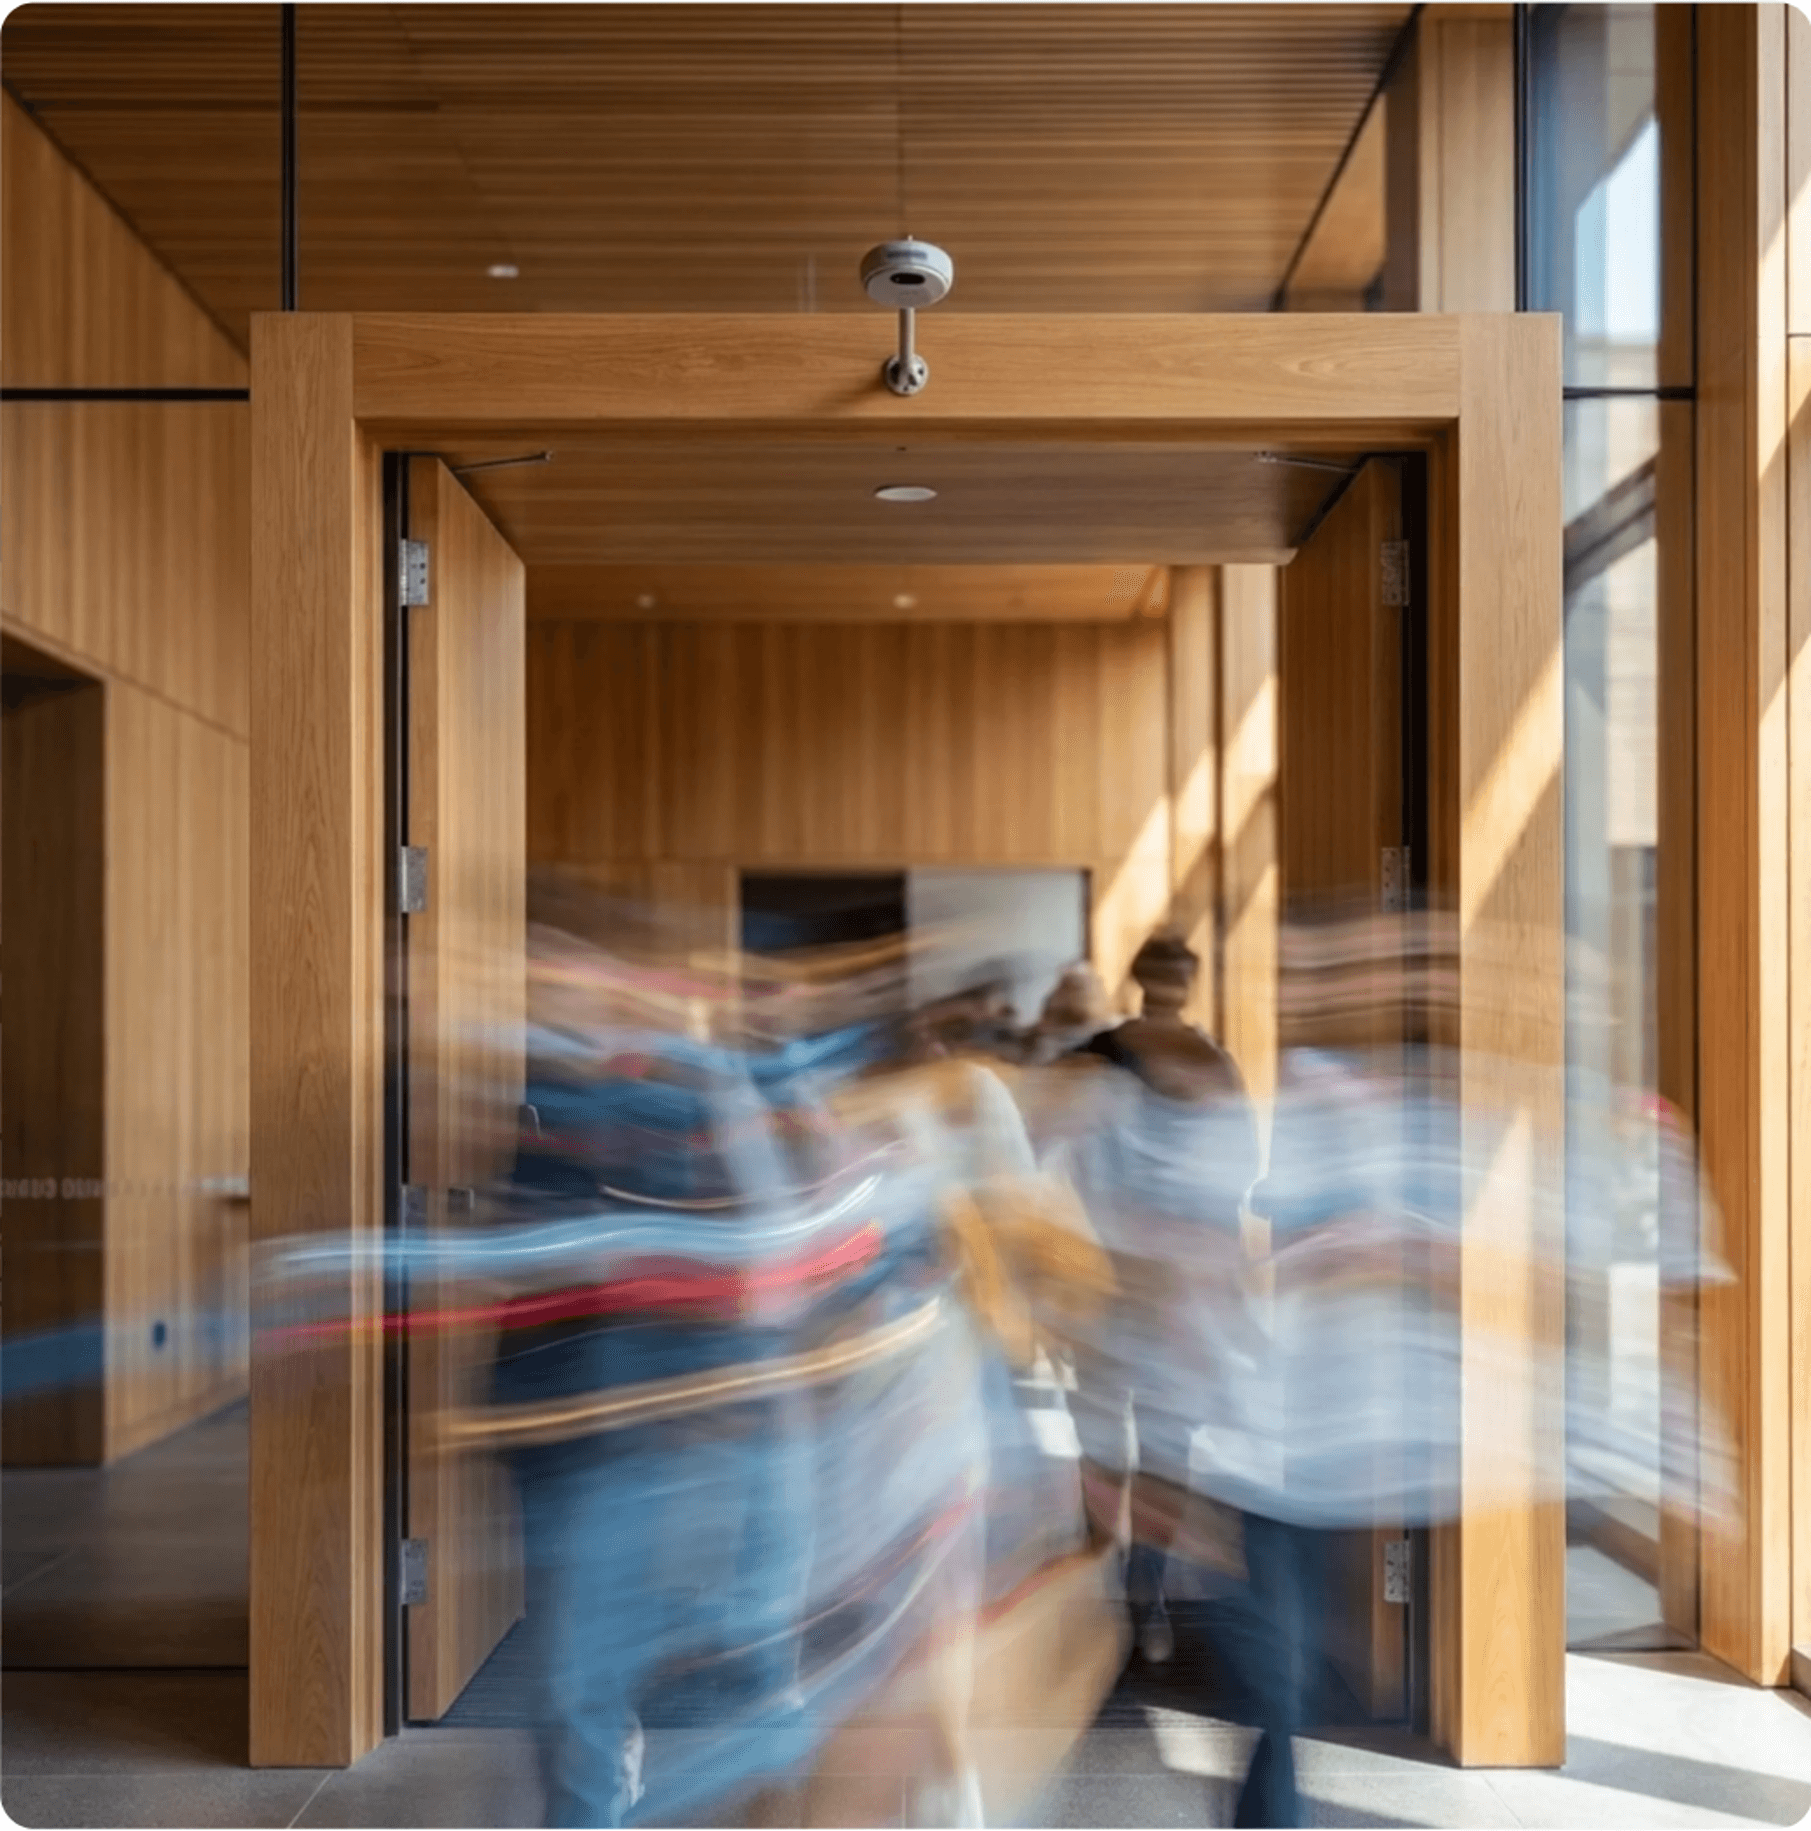
Alright, that covers data protection. Now the next thing: why is your IT colleague asking you questions about how the sensors connect to the network, and throwing around abbreviations like LoRaWAN, PoE, MQTT, IP, and more? This is because they want to know how the sensors will transmit data to the online platform and if there is any interference with existing university networks: the Wi-Fi network or the wired (IP) network.
Our way to deal with this question is to provide options. The easiest option, especially in pilots, is to work around institutional networks. By placing a few gateways, we establish our own secure network which safely captures the sensor data and sends it to our platform. Alternatively, we have done deployments via institutional LoRaWAN and wired IP networks, routing the sensor data in the way desired by the institution.
Cybersecurity
A concern related to the previous one of connectivity, is cybersecurity. What measures are taken to protect systems, networks, devices against unauthorized access, theft, and attacks? There are different certifications and qualifications in this area to demonstrate compliance, both self-assessed and independently audited: CSA Star, ISO 27001 and Cyber Essentials, to name a few.
At Pleq, we take cybersecurity very seriously, and we have a detailed documentation of the security measures we have taken and continue to take to ensure a high level of protection. This pertains to the entire data chain, from initial data collection to visualization.
Digital sovereignty and autonomy
Then, the next thing might be digital sovereignty and autonomy. Is that also an issue in IT systems nowadays? Yes, it is! Your IT colleague wants to avoid the risk that foreign states can cut off essential services, and that conflicting privacy rules across borders may impact agreements made here. Moreover, they want to avoid vendor lock-in, by retaining ownership of the collected data. How do you ensure that?
At Pleq, we’ve designed our solution towards this objective. We want data ownership to remain with our clients. By providing export functionalities and an open API stack, we give our clients access to their data at all times. Furthermore, you have the right to have all collected data deleted at the end of your contract. Together, this ensures data ownership remains with you at all times. With regards to sovereignty, we operate on the principle that our solution is EU-made. Our sensing technology is fabricated in the EU, and our data is hosted in the EU.
Moving towards implementatation: FAQ
You might be thinking: okay, thanks for the clarification, but how do I now convince IT?
Here are some frequently asked questions:
1. Is your solution GDPR-compliant?
Yes. Our sensors use time-of-flight technology, which cannot be used to detect individuals or characteristics of individuals. We ingest scheduling and/or booking data, but avoid the use of personal data such as the name of the meeting organizer or the teacher of the scheduled activity.
2. How do you ensure safe network connectivity?
We make use of LoRaWAN networks to transmit data from sensors to our cloud platform. All data is encrypted at the sensor, and only numerical data is transmitted by the sensor. Only the PLEQ backend can decrypt the data that is transmitted over the network. In addition, all sensors, gateways and the backend system accounts have strong, unique passwords that are stored in a password vault.
3. What measures have you taken to protect yourself against unwanted access?
In addition to the data encryption and password policies introduced in question 2, we have a wide range of measures in place. Our sensors are not allowed to transmit data, and have no network services that can be accessed from the outside. Our gateways communicate exclusively over encrypted, outbound protocols, they block inbound connections, and no ports are open for unwanted access. Our back-end runs on EU-hosted data centers that are ISO 27001, SOC 2 and GDPR certified.
4. How do you ensure data-ownership for your clients and limit vendor lock-in?
All collected data is stored on EU-hosted data centers and can be accessed at any point by you, via our Export functionalities in the platform. If our contract ever ends, we will transfer all collected data to you and delete the data from our servers, following a standardized procedure.
5. Where can I find more information on all these issues?
No worries – we’ve got you covered. We can send you our Privacy and Security pack, which contains all the information you (or your IT colleagues) need. Also, feel free to contact us at info@pleqcampus.nl


